SOC 1
Prove to your clients' auditors that their financial data is in safe hands. SSAE 18 reports with dual US-Swiss credibility.
Learn More →From Zurich to Silicon Valley
Auditsuisse is a US and Swiss licensed SOC 2 audit firm for SaaS and technology companies. Explore published fees, compare report types, and discuss the scope your customers require.


Identify the report type, systems and criteria your customers expect. Review the published pricing assumptions, then confirm the engagement scope before work begins.
Our Services
Expert audit services tailored to your industry, scale, and regulatory requirements.
Prove to your clients' auditors that their financial data is in safe hands. SSAE 18 reports with dual US-Swiss credibility.
Learn More →SOC 2 Type I and Type II examinations of controls relevant to your selected Trust Services Criteria. Explore the scope, process, and report options.
Learn More →Put your security posture on your website. A publicly shareable seal of trust from the same SOC 2 engagement.
Learn More →Navigate EU data protection with a Swiss-headquartered team that lives and breathes cross-border compliance.
Learn More →Assess policies, procedures, and safeguards against applicable HIPAA requirements. Review the assessment scope, findings, and remediation priorities.
Learn More →Independent assurance over ESG, sustainability, and non-financial reporting under the internationally recognized IAASB standard.
Learn More →International assurance reports on controls at service organizations — the global standard trusted by auditors across jurisdictions.
Learn More →Manual, OSCP-certified pen tests mapped to OWASP Top 10 and SANS Top 25 — signed reports your auditors accept and customers trust.
Learn More →Related guide: SOC 1 vs SOC 2
Understanding SOC 2
A SOC 2 audit is an independent examination of a service organization's controls, conducted exclusively by a licensed CPA firm under the AICPA's Trust Services Criteria. It evaluates how a company protects customer data across five categories: security, availability, processing integrity, confidentiality, and privacy. For the requirements and the process, read what SOC 2 compliance is, or see our SOC 2 audit services.
Big 4 experience. Boutique speed. We built Auditsuisse for organizations that refuse to choose between rigor and efficiency — bringing experience and trusted precision, dual-jurisdiction credibility, and a streamlined methodology that larger firms can't match.
Rigorous testing. Every finding documented. Clear reporting.
US, EMEA, APAC, LATAM — one firm, one methodology, one quality standard.
Define the scope, preparation tasks and reporting milestones at the start of your engagement.
A senior auditor who knows your stack, assigned from day one.
Our Leadership
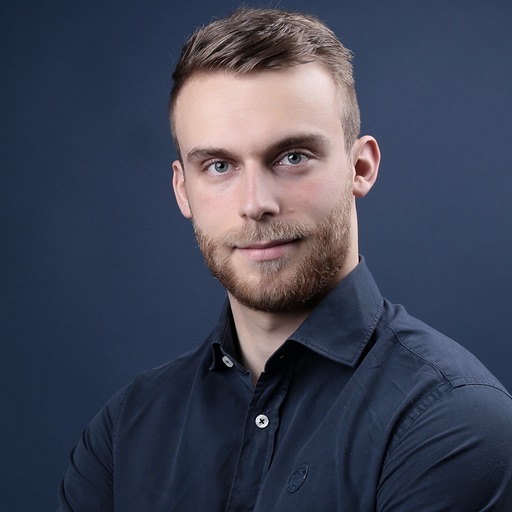
Director
Sébastien is the Director of Auditsuisse Assurance. He is a certified Swiss CPA (Wirtschaftsprüfer, RAB license n°114662) and US CPA (license n°034634), with a specialization in Information Systems and Controls (ISC). He holds a Master's degree in Accounting, Control and Finance from the University of Lausanne.
With a background in audit within a Big Four firm, where he worked for nearly five years, he has developed solid expertise working with both SMEs and international groups. He specializes in SOC 2 and cybersecurity, supporting technology-driven companies in the design, implementation, and evaluation of their control environments.
Learn More About Our Team →Get Started
Tell us your timeline, your framework, and your deal on the line — we'll tell you exactly how we get you there.